Answers to the questions we hear most from healthcare teams considering a HubSpot Audit
What Does the HubSpot HIPAA Audit Cover?
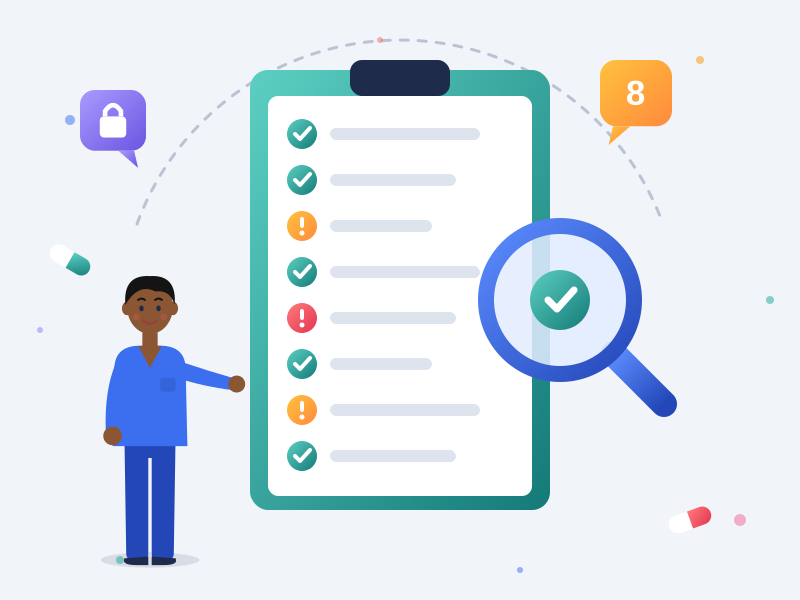
We review your portal across eight areas, each rated low, moderate, high or critical.
-
Account foundation: Enterprise subscription, Sensitive Data settings, HIPAA status, BAA acceptance and data center location
-
Data placement: where sensitive data lives, including properties, notes, emails, call logs, attachments and the files tool
-
Access control: user permissions, field-level restrictions, super admins and two-factor authentication
-
Integrations: which connected tools send or receive sensitive data, and whether each is covered by a BAA or DPA
-
Automation and communications: workflows, sequences, notifications and templates that could expose health details
-
Forms and website: sensitive form fields, HubSpot tracking code and ad pixels on intake, appointment and condition pages
-
AI use: how Breeze and any outside AI tools interact with sensitive data
-
Governance and regional rules: documentation, audit log reviews, data residency and privacy laws outside the US, such as PHIPA, PIPEDA, GDPR and the Cayman Data Protection Act
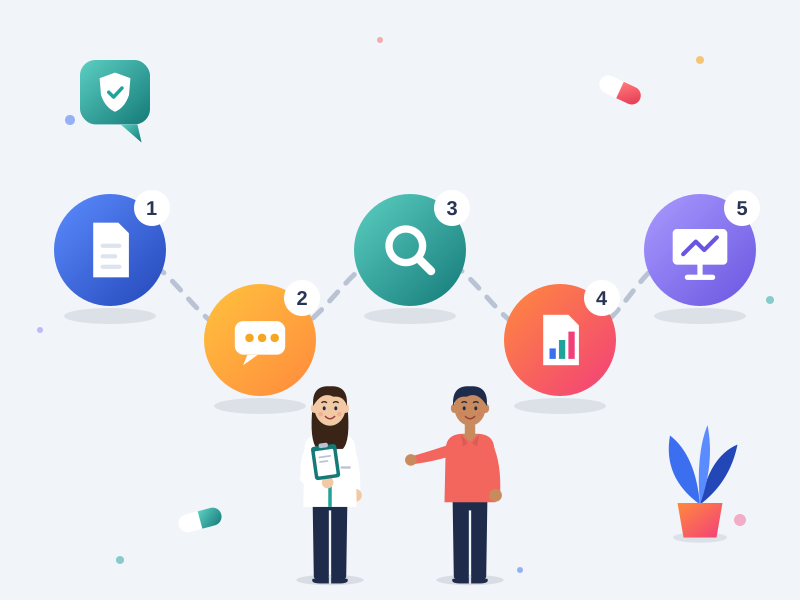
How Does the Audit Work? 5 Steps From BAA to Readout
-
Agreement and access. We sign a Business Associate Agreement (US) or data processing agreement (other regions) before anything else. You create a read-only user for us, and we focus on configuration and metadata wherever possible.
-
Kickoff call (30 minutes). We meet your HubSpot admin to understand your goals, connected systems, the regions you operate in and any upcoming security reviews.
-
Portal review. Our senior HubSpot team works through all eight areas in your portal.
-
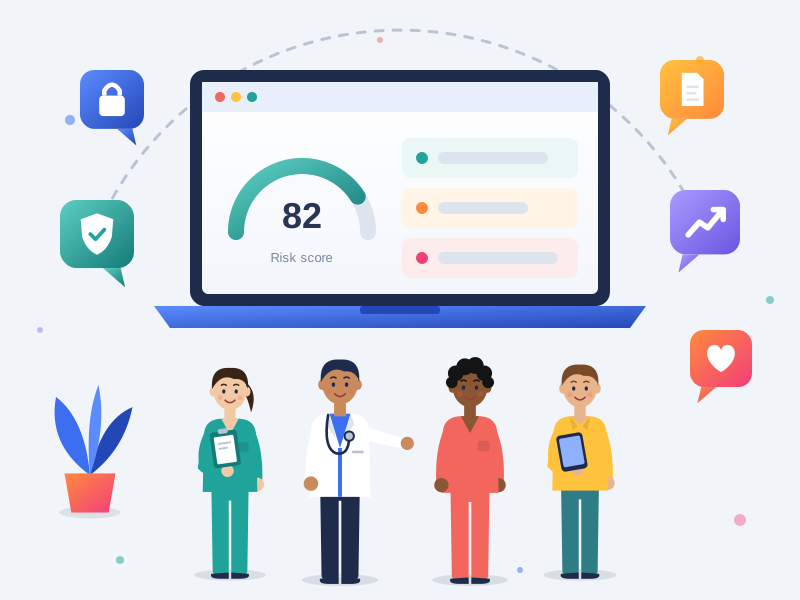
Report. You receive your Compliance Risk Score, a rating for each area, findings with evidence and a prioritized fix list. Findings describe where types of data sit, never the data itself.
-
Readout (45 minutes). We walk your decision-makers and your compliance or security lead through the results and answer questions. Our read-only access is removed at the end.
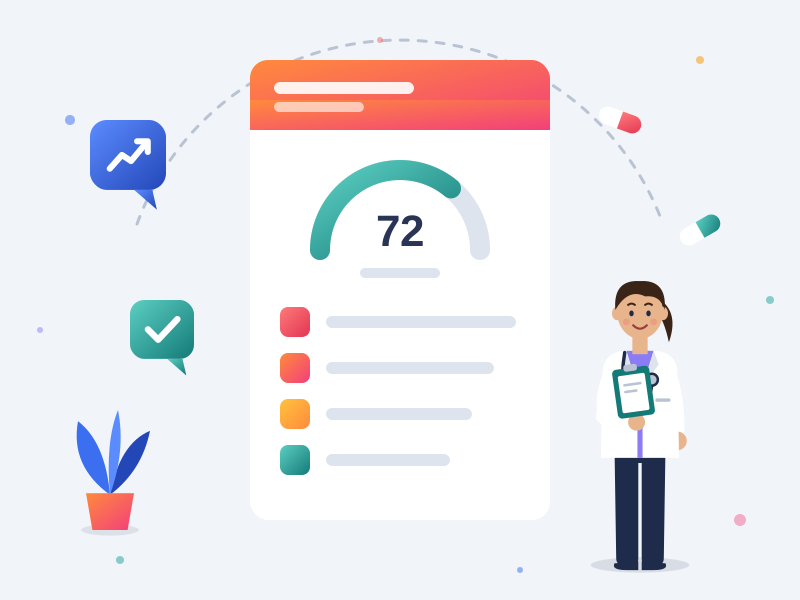
What You Get: Your HubSpot Compliance Risk Score and Fix List
-
A Compliance Risk Score from 0 to 100, so leadership can see where the portal stands at a glance.
-
A rating for each of the eight areas, showing where the risk is concentrated.
-
Findings with evidence, written so your compliance or security team can use them in their own reviews.
-
A prioritized fix list, ranked by risk and effort, so you know what to do first.
-
A 45-minute readout with our team to talk through the results.
The report is our professional assessment of your HubSpot configuration. It isn't legal advice or a certification, and we recommend reviewing your obligations with qualified counsel.
If you'd like help fixing what we find, we can scope a remediation project from the fix list, from Sensitive Data setup to HubSpot integrations and workflow cleanup.
Who Needs a Healthcare CRM Audit?
The audit is built for healthcare organizations that use HubSpot Professional or Enterprise, or are planning to move to Enterprise:
-
Healthcare providers and multi-location clinics handling patient inquiries, referrals and appointments
-
Treatment and behavioral health organizations with sensitive inquiries and stricter consent rules, including 42 CFR Part 2 in the US
-
Health tech, digital health and healthcare SaaS companies whose customers expect proof that patient data is handled properly
-
Medtech and life sciences teams running patient programs or healthcare professional outreach in HubSpot
It's especially useful before a security review, a vendor questionnaire, a HubSpot renewal or upgrade, a new integration, or expansion into a new country.
Learn more about our HubSpot for healthcare services.
HubSpot HIPAA Audit FAQs
What is a HubSpot HIPAA audit?
A HubSpot HIPAA audit is a review of how your HubSpot portal handles protected health information. It checks your account setup, where sensitive data is stored, who can access it, which connected tools receive it, and how automation and forms handle it, then gives you a risk score and a prioritized fix list.
Do you sign a BAA before the audit?
Yes. We sign a Business Associate Agreement before accessing a portal that may hold protected health information. Outside the US, we sign a data processing agreement instead.
Will you see our patient data?
We review your portal with a read-only user and focus on configuration and metadata, such as settings, property definitions, permissions, integrations and workflows. Our reports describe where types of data sit, never the data itself.
How long does the audit take?
Most audits take about two to three weeks from the signed agreement to the readout, depending on the size of your portal and how quickly access is set up.
Is the audit only for HIPAA?
No. HIPAA applies in the US, and we also review your setup against privacy laws in other regions, including PHIPA and PIPEDA in Canada, GDPR in the UK and EU, and the Data Protection Act in the Cayman Islands.
What happens after the audit?
You keep the report and fix list, whether or not you work with us. If you'd like help, we can scope a remediation project based on the findings.